Runtime security grounded in what runs
Founded in 2023 in San Francisco. We use eBPF to map live dependencies, detect reachable CVEs and anomalies, and block exploits without code changes.
Security should measure what actually runs
Static and software composition analysis show packages and known CVEs. They do not show what executes, which call paths are reachable, or whether suspicious behavior is happening now.
We saw teams patch libraries that never ran in production while missing behavior during execution. Oligo gives decision makers live dependency and kernel signals when pressure is high.
Runtime behavior is our ground truth. eBPF observes the kernel without application code changes.
The team behind the work
Small, focused team with deep expertise in kernel observability, runtime security, and developer growth.
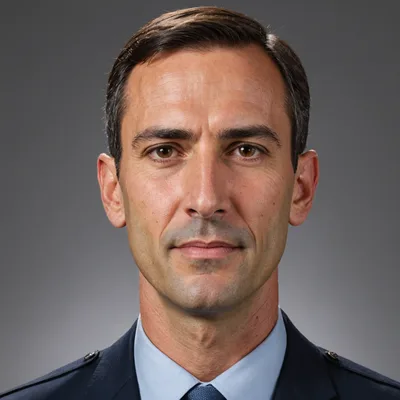
Focuses on kernel observability, runtime detection, eBPF program design, and BPF CO-RE portability across kernel versions.
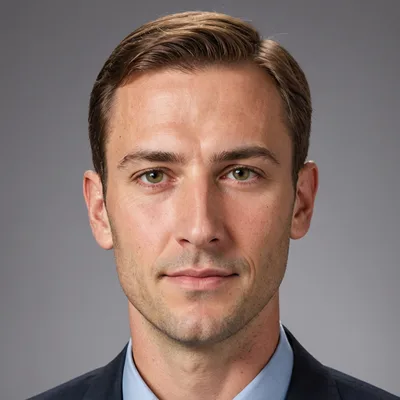
Builds Linux kernel observability systems and eBPF-adjacent open-source tooling. Leads the signal attribution pipeline, tying each alert to the library and code path that triggered the syscall, and develops the behavioral baseline engine.
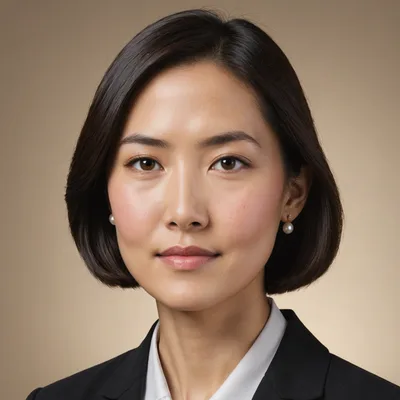
Focuses on developer marketing and community growth for B2B developer tools and security, helping AppSec practitioners understand and adopt runtime security capabilities.
Runtime visibility is a design constraint
We start with observable runtime behavior, not static models. eBPF gives kernel visibility without application code changes.
Every Oligo design decision asks what the kernel observed and whether the signal helps the person receiving the alert.
We are bootstrapped and intentionally small. We build kernel instrumentation and share research in the Security Lab because technical depth builds trust.
Want to discuss our technical approach?
We prefer technical conversations to demos. Ask us about the eBPF architecture.